TheJavaSea.me Leaks AIO-TLP371: Understanding the Online Claims and Security Risks
TheJavaSea.me Leaks AIO-TLP371
TheJavaSea.me leaks AIO-TLP371 is a search term associated with online discussions about alleged leaked files, digital archives, and information shared through internet platforms. People searching for this phrase may want to understand what AIO-TLP371 means, why the identifier is attracting attention, and whether it is connected to a cybersecurity incident. However, the exact contents, origin, and authenticity of the material associated with this term have not been independently established. Understanding the subject therefore requires separating available information from assumptions and examining the broader risks associated with alleged data leaks.
The phrase combines a website name with a technical-looking identifier. Similar naming conventions frequently appear in internet conversations about bundled files, software distributions, and stored digital resources. Some descriptions associate AIO-TLP371 with a bundled collection of files, but the label itself does not confirm what those files contain or whether they were obtained through unauthorized access. Without reliable evidence, it would be inaccurate to describe the collection as a confirmed database breach or claim that it contains specific personal information.
The topic also appears alongside related search terms, including thejavasea.me leaks aio-tlp370, thejavasea.me leaks aio-tlp476, thejavasea.me leaks aio-416, thejavasea.me leaks aio-tlp513, thejavasea.me leaks aio-tlp, thejavasea.me leaks aio-tlp287, and thejavasea.me leaks aio-tlp142. These phrases suggest that users are exploring a broader group of identifiers, but their appearance together does not establish that they represent connected incidents. Examining the terminology, evaluating the available claims, and understanding practical cybersecurity precautions can help readers approach the subject more responsibly.
What Is TheJavaSea.me?
TheJavaSea.me is the website name appearing in the search phrase associated with AIO-TLP371. In discussions about alleged online leaks, a domain may become a point of interest because users encounter references to files, collections, or shared information connected with it. However, a website’s name appearing in an article does not establish the authenticity of the material being discussed or confirm that a particular security incident has occurred.
When investigating a website associated with alleged leaked content, it is important to consider what can actually be verified. The availability of a webpage, the circulation of a filename, and the publication of an article are different from independently confirming the origin of a dataset. Reliable conclusions require evidence connecting the material to a source and explaining why its contents should be considered authentic.
People should remain cautious when accessing unknown websites that claim to provide restricted or exclusive digital material. Some websites use attention-grabbing descriptions to encourage visitors to click links, download archives, or submit personal information. These practices can create security and privacy risks, particularly when the website’s ownership and purpose are unclear. It is sensible to avoid providing credentials, payment information, or unnecessary permissions to a site that has not been established as trustworthy.
What Does AIO-TLP371 Mean?
The identifier AIO-TLP371 is the central element of the search phrase. AIO commonly stands for All-In-One, a term used in technology to describe a package containing multiple resources or components. Depending on the context, it may refer to a software bundle, a collection of documents, or a group of files assembled into one package. Nevertheless, the abbreviation alone does not establish the actual contents of the material associated with AIO-TLP371.
The meaning of TLP371 is less certain. It appears to function as part of an identifier, but its exact purpose has not been authoritatively documented. The number could be an informal label used to distinguish one item from another, but there is insufficient evidence to confirm that interpretation. The identifier alone does not establish the order of a release, the seriousness of an incident, or the number of records potentially affected.
Recognizing this difference matters because identifiers that appear technical may suggest a level of accuracy that the available evidence does not support. A label may appear systematic without following a recognized classification method. Readers should therefore avoid drawing conclusions about the origin, size, or significance of a collection simply by examining its name.
The letters TLP also have a separate meaning in cybersecurity. The Traffic Light Protocol is used to communicate how sensitive information may be shared. Its standard classifications are TLP, TLP, TLP, and TLP. TLP371 is not one of these official designations. The presence of the letters TLP in AIO-TLP371 does not demonstrate that the identifier belongs to the formal protocol.
Why Is AIO-TLP371 Being Discussed Online?
Online searches for terms associated with alleged data leaks may increase for a range of reasons. A particular identifier may appear in forum discussions, blog posts, social media updates, or search results. Once people begin searching for it, additional publishers may create content explaining the term. This can increase its visibility even when the available information about the underlying material remains limited.
Another reason is the way technical subjects are presented online. Terms that resemble database identifiers or release labels can attract attention because they suggest that a specific collection exists. Users may search for the phrase to determine whether it refers to software, personal information, a cybersecurity incident, or another type of digital material. However, the popularity of a phrase does not establish the accuracy of the claims associated with it.
Some articles may also repeat descriptions from other websites. When several pages use similar wording, readers might assume that the claims have been independently confirmed. In reality, multiple articles can rely on the same unverified statement. A more reliable assessment considers whether a report presents original evidence, explains the source of its information, and distinguishes confirmed details from speculation.
For this reason, the discussion surrounding AIO-TLP371 should be approached as a subject requiring verification rather than as proof of a specific breach. Understanding why a phrase is circulating is useful, but determining whether the underlying claims are accurate requires additional evidence.
Understanding the Related AIO-TLP Identifiers
Several related phrases appear in searches associated with TheJavaSea.me. These include AIO-TLP370, AIO-TLP476, AIO-416, AIO-TLP513, AIO-TLP287, and AIO-TLP142. Their similar naming structure may suggest that they belong to the same general discussion, but there is not enough verified information to establish that they represent separate archives or versions of one collection.
TheJavaSea.me Leaks AIO-TLP370
AIO-TLP370 differs from AIO-TLP371 by one number. Although this difference might lead readers to assume that the two identifiers represent consecutive releases, the numbering alone cannot establish such a relationship. There is no reliable basis for claiming that one contains an earlier version of the same material or that the two collections have different contents.
TheJavaSea.me Leaks AIO-TLP476
AIO-TLP476 is another related search phrase. Its higher number does not necessarily indicate a more recent release, a larger archive, or a more serious security incident. Without documentation explaining the naming system, the number should be treated as an identifier rather than evidence about the material itself.
TheJavaSea.me Leaks AIO-416
AIO-416 uses a slightly different format because it does not include the full TLP sequence found in some of the other phrases. This difference may simply reflect an alternative naming convention, but its meaning remains uncertain. It should not be assumed to represent a different category of leaked information without supporting evidence.
TheJavaSea.me Leaks AIO-TLP513
AIO-TLP513 appears in the same general group of search terms. However, its relationship to AIO-TLP371 has not been authoritatively established. Claims that the two identifiers contain connected information, belong to the same release series, or describe separate confirmed breaches would require independent verification.
TheJavaSea.me Leaks AIO-TLP287 and AIO-TLP142
These two identifiers are also associated with related searches. Their numbering does not establish a timeline or explain what the alleged collections contain. Every term should be assessed on its own merits, considering the available evidence about where it originated and what information it allegedly describes.
The broader term AIO-TLP may refer to the general subject rather than one specific identifier. Taken together, these phrases demonstrate how related keywords can develop around an online topic, but they do not constitute a verified record of cybersecurity incidents.
Potential Risks of Visiting Leak-Related Websites
Although the details surrounding AIO-TLP371 remain uncertain, visiting unfamiliar websites or downloading unknown files can expose users to genuine cybersecurity risks. These risks depend on the website, the files being offered, and the actions a visitor takes. It is therefore useful to understand the main threats without assuming that every risk has been confirmed in connection with this particular identifier.
Malware and Unsafe Downloads
One concern is the possibility of malicious software being distributed through files advertised as documents, archives, or applications. A download may appear legitimate while containing an executable designed to compromise a device. In other cases, a link may redirect visitors to another website that attempts to install unwanted software or obtain sensitive information.
Users should not assume that a file is safe because its name includes a technical identifier or because a website describes it as a useful collection. Unknown files should not be opened or executed simply to investigate a trending topic. Keeping software updated and downloading applications only from trusted sources can reduce exposure to common threats.
Password Exposure and Account Security
Alleged data leaks sometimes raise concerns about the exposure of login credentials. If genuine passwords become accessible to unauthorized individuals, accounts may be vulnerable to misuse. The risk becomes greater when the same password is used for several services because a single compromised credential may provide an opportunity to access other accounts.
There is insufficient verified information to state that AIO-TLP371 contains working passwords. Nevertheless, the possibility of credential exposure highlights the importance of using unique passwords and enabling multi-factor authentication. These measures help limit the consequences of an exposure, regardless of whether a particular online claim is eventually confirmed.
Phishing and Online Fraud
Websites discussing alleged leaks may attract people who are curious about the contents of a collection. Scammers can take advantage of that interest by offering access through misleading links, fake registration forms, or payment requests. A page might ask visitors to enter an email address, provide login credentials, or download a special tool before displaying information.
Such requests should be treated cautiously, especially when the website’s identity and purpose are unclear. Legitimate security investigations do not require users to surrender unrelated account passwords or recovery codes to unfamiliar websites. Visitors should also be careful with unexpected messages claiming that their information has been exposed and demanding immediate action.
Privacy and Personal Information
If a data collection genuinely contains personal records, unauthorized distribution can create risks for the people involved. Depending on the information exposed, those risks may include identity misuse, impersonation, targeted scams, and unwanted disclosure of private details.
However, these consequences depend on the actual contents of the material. Without verified evidence, it would be inappropriate to claim that AIO-TLP371 contains particular records or has affected a specific group of people. Responsible discussion should explain potential risks while clearly distinguishing them from confirmed outcomes.
How to Evaluate Claims About AIO-TLP371
Assessing the credibility of information about an alleged leak begins with examining the evidence. An article should explain what is known, identify the basis for its claims, and acknowledge important gaps in the available information. A webpage offers limited credibility when it merely repeats a search term or labels a collection as authentic without providing verifiable details about its source.
The source of the alleged information is another important consideration. If a report connects a collection to a particular company or service, there should be evidence supporting that connection. A filename, screenshot, anonymous forum post, or copied description may indicate that a claim is circulating, but it does not independently prove that the underlying information is authentic.
Readers should also distinguish the publication date of an article from the date of an alleged incident. A collection may be discussed months or years after the information was originally obtained. Similarly, a newly created webpage may repeat older claims without documenting a new event. Establishing a timeline requires information about the original source, the alleged exposure, and any subsequent investigation.
Another useful approach is to examine whether different reports offer genuinely independent evidence. Identical claims appearing across multiple websites do not necessarily represent independent verification of the information. Reliable confirmation may be provided through trustworthy news coverage, verified investigative findings, or an official statement from the organization concerned.
Above all, investigating these claims should never require opening questionable downloads or sharing sensitive details with untrusted platforms. The priority is to assess the available evidence without exposing personal accounts or devices to potential security threats.
Practical Ways to Keep Personal Information Secure
Use Strong and Unique Passwords
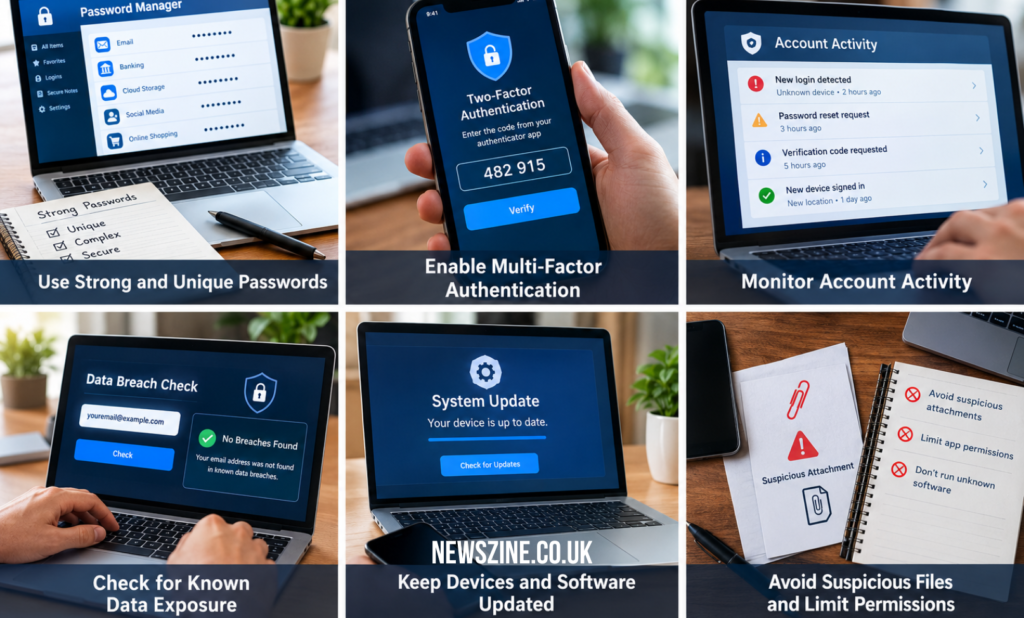
People concerned about AIO-TLP371 or similar leak-related topics can take practical steps to improve their digital security. The first is to review password practices. Important accounts should have unique passwords, particularly email accounts, financial services, cloud storage, and platforms that can be used to reset other passwords. A reliable password manager helps users generate strong, distinct passwords and keep their login details safely organized across multiple accounts.
Enable Multi-Factor Authentication
Using multi-factor authentication helps prevent unauthorized account access by requiring users to confirm their identity through an additional security method. This feature requires an additional verification step during sign-in and can make unauthorized access more difficult when a password has been exposed. Authenticator applications and security keys are useful options where supported. Users should also protect their recovery email addresses and telephone numbers because these may be used to regain access to other accounts.
Monitor Account Activity
Account monitoring is equally important. Unexpected login notifications, unfamiliar devices, unrequested verification codes, and password-reset messages can indicate suspicious activity. If a user notices an unfamiliar sign-in, they should access the service through its official website or application, review active sessions, remove unauthorized access, and update the affected credentials.
Check for Known Data Exposure
Users may also check reputable breach-notification services to determine whether their email addresses appear in known exposure records. These services have limitations and cannot confirm that an account has never been compromised. A missing result does not guarantee complete safety, but a confirmed match may help users identify accounts that require additional attention.
Keep Devices and Software Updated
Finally, keeping operating systems, browsers, and applications updated helps protect devices against known security weaknesses. Users should avoid suspicious attachments, limit unnecessary application permissions, and refrain from running unknown software. If a suspicious file has already been executed, it is sensible to scan the device with reputable security software and secure important accounts from a separate, trusted device if compromise is suspected.
Legal and Ethical Considerations of Alleged Data Leaks
Reports of possible data exposure also highlight concerns surrounding personal privacy, lawful access, and the ethical use of digital records. A file that becomes accessible online is not necessarily lawful to distribute or use. It may contain confidential business records, personal information, or material obtained without permission. The legal consequences of accessing or sharing such information depend on the circumstances and the applicable jurisdiction.
There are also ethical reasons to avoid spreading potentially stolen material. Republishing private records can increase their exposure and make it more difficult for affected individuals to protect themselves. Even when a collection is discussed publicly, its contents may still involve people who did not consent to the disclosure.
Cybersecurity discussions can remain informative without reproducing private information or directing readers toward unauthorized files. Explaining the uncertainty surrounding an alleged incident, identifying common risks, and recommending appropriate protective measures can help readers understand the subject without contributing to further harm.
Why Responsible Reporting Matters
Accurate reporting is particularly important when a topic involves alleged data exposure. Strong claims about a breach can cause unnecessary concern if they are not supported by evidence. On the other hand, dismissing a credible warning without examining it can prevent people from taking appropriate precautions. Responsible coverage must balance these concerns by explaining what is established, what remains uncertain, and what actions readers can reasonably take.
In the case of AIO-TLP371, the central challenge is the lack of independently established information about the identifier’s origin and contents. Articles that describe it as a confirmed breach, provide exact figures, or identify specific victims should be assessed carefully unless they offer reliable supporting evidence. The same standard should apply to the related AIO-TLP labels.
Clear reporting also helps readers distinguish general cybersecurity advice from claims about a particular event. Password protection, multi-factor authentication, and safe browsing are useful practices in many situations, but recommending them does not prove that a specific collection has compromised user information. Maintaining this distinction makes online information more accurate and useful.
Conclusion
TheJavaSea.me leaks AIO-TLP371 is a search term associated with discussions about alleged leaked digital material. Nevertheless, no independent verification has clarified what the identifier represents, where the material originated, or what it contains. Its technical format and association with similar search terms are not enough to prove that a particular data breach occurred or identify any affected individuals.
The related phrases AIO-TLP370, AIO-TLP476, AIO-416, AIO-TLP513, AIO-TLP287, and AIO-TLP142 should be approached with the same caution. Their similarities may reflect a shared naming pattern or online discussion, but their relationships cannot be established from the numbers alone. Any allegation must be supported by credible information before it can be accepted as an established fact.
For readers, the most useful response is to approach unfamiliar websites carefully, avoid suspicious downloads, protect account credentials, and evaluate online claims before sharing them. Unique passwords, multi-factor authentication, account monitoring, and regular software updates can reduce common cybersecurity risks. By distinguishing verified information from speculation and respecting the privacy of others, readers can understand topics such as AIO-TLP371 without exposing themselves to unnecessary security or privacy problems.